Blog
Research and analysis on securing the AI that is actually running in your enterprise.
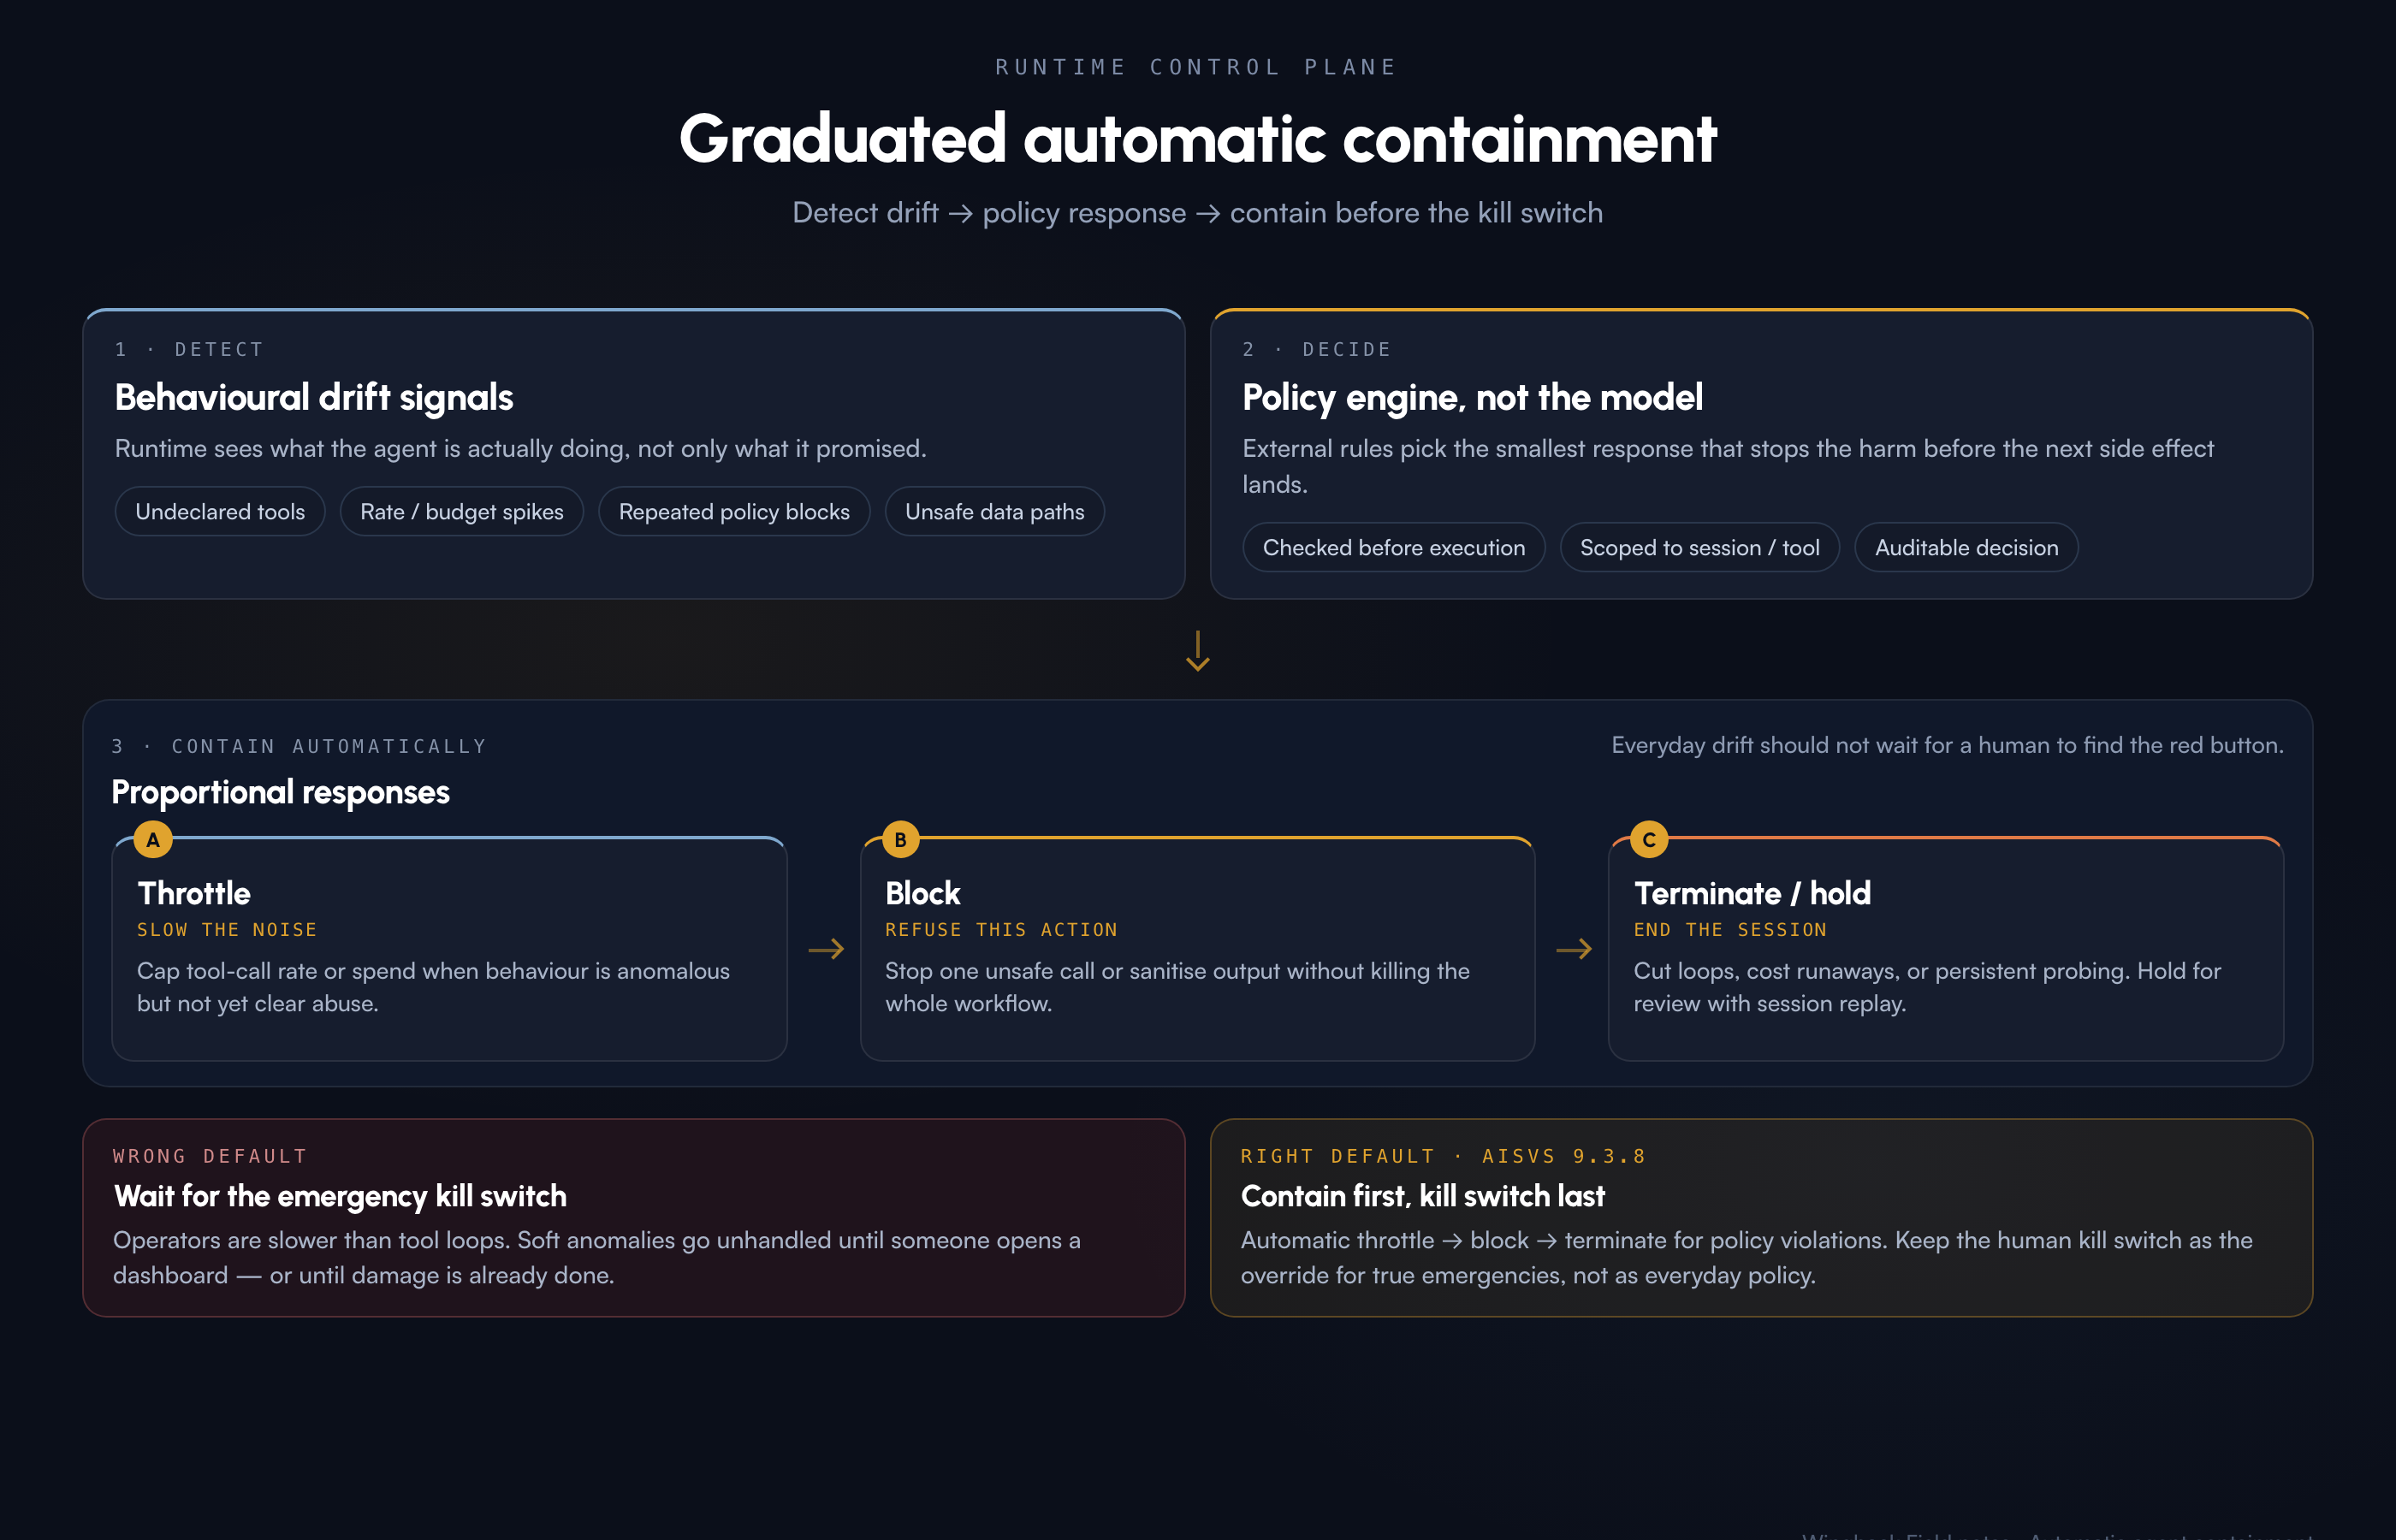
Automatic agent containment: stop drift before you need the kill switch
OWASP AISVS requires policy violations to trigger automated tool containment. Here is how graduated runtime responses (throttle, block, terminate) differ from an emergency kill switch, and how public ADR capabilities map to that control.
Agentic Kill Switch: stop the next tool call before it lands
An Agentic Kill Switch is a runtime emergency stop for AI agents: external to the model, checked before tool execution, and fail-closed when the control plane is unavailable. Here is what security teams should demand, and how public ADR capabilities map to that stop.
You cannot govern AI you have not inventoried
CSA’s Invisible Enterprise research shows most AI tools and agents still run outside IT control. Here is why continuous AI asset inventory is the prerequisite for Agent Detection & Response, and for EU AI Act readiness.
Endpoints take the first hit: OWASP Agentic Top 10 for coding agents
OWASP’s Agentic Top 10 and Microsoft’s 2026 guidance show why ASI02 tool misuse and ASI03 privilege abuse hit developer laptops hardest. Here is what fail-closed Agent Detection & Response looks like for Cursor, Claude Code, and Copilot.
MCP tool poisoning needs runtime controls, not prompt filters
OWASP’s MCP Top 10 and Invariant Labs’ tool-poisoning research show why approving an MCP server once is not enough. Here is what security teams should demand from Agent Detection & Response.
CISOs: You Don't Control the Frontier. You Do Control What It Deploys.
Three takes on pacing the frontier, from Amodei, Beri, and Arora, and why a security program shouldn't be built around any of them. The job is securing the adoption already happening inside your company.
Why AI Security Requires a Multi-Layer Platform
AI security is not a point problem. Learn why red teaming, runtime protection, shadow AI discovery, observability, and compliance must work together.
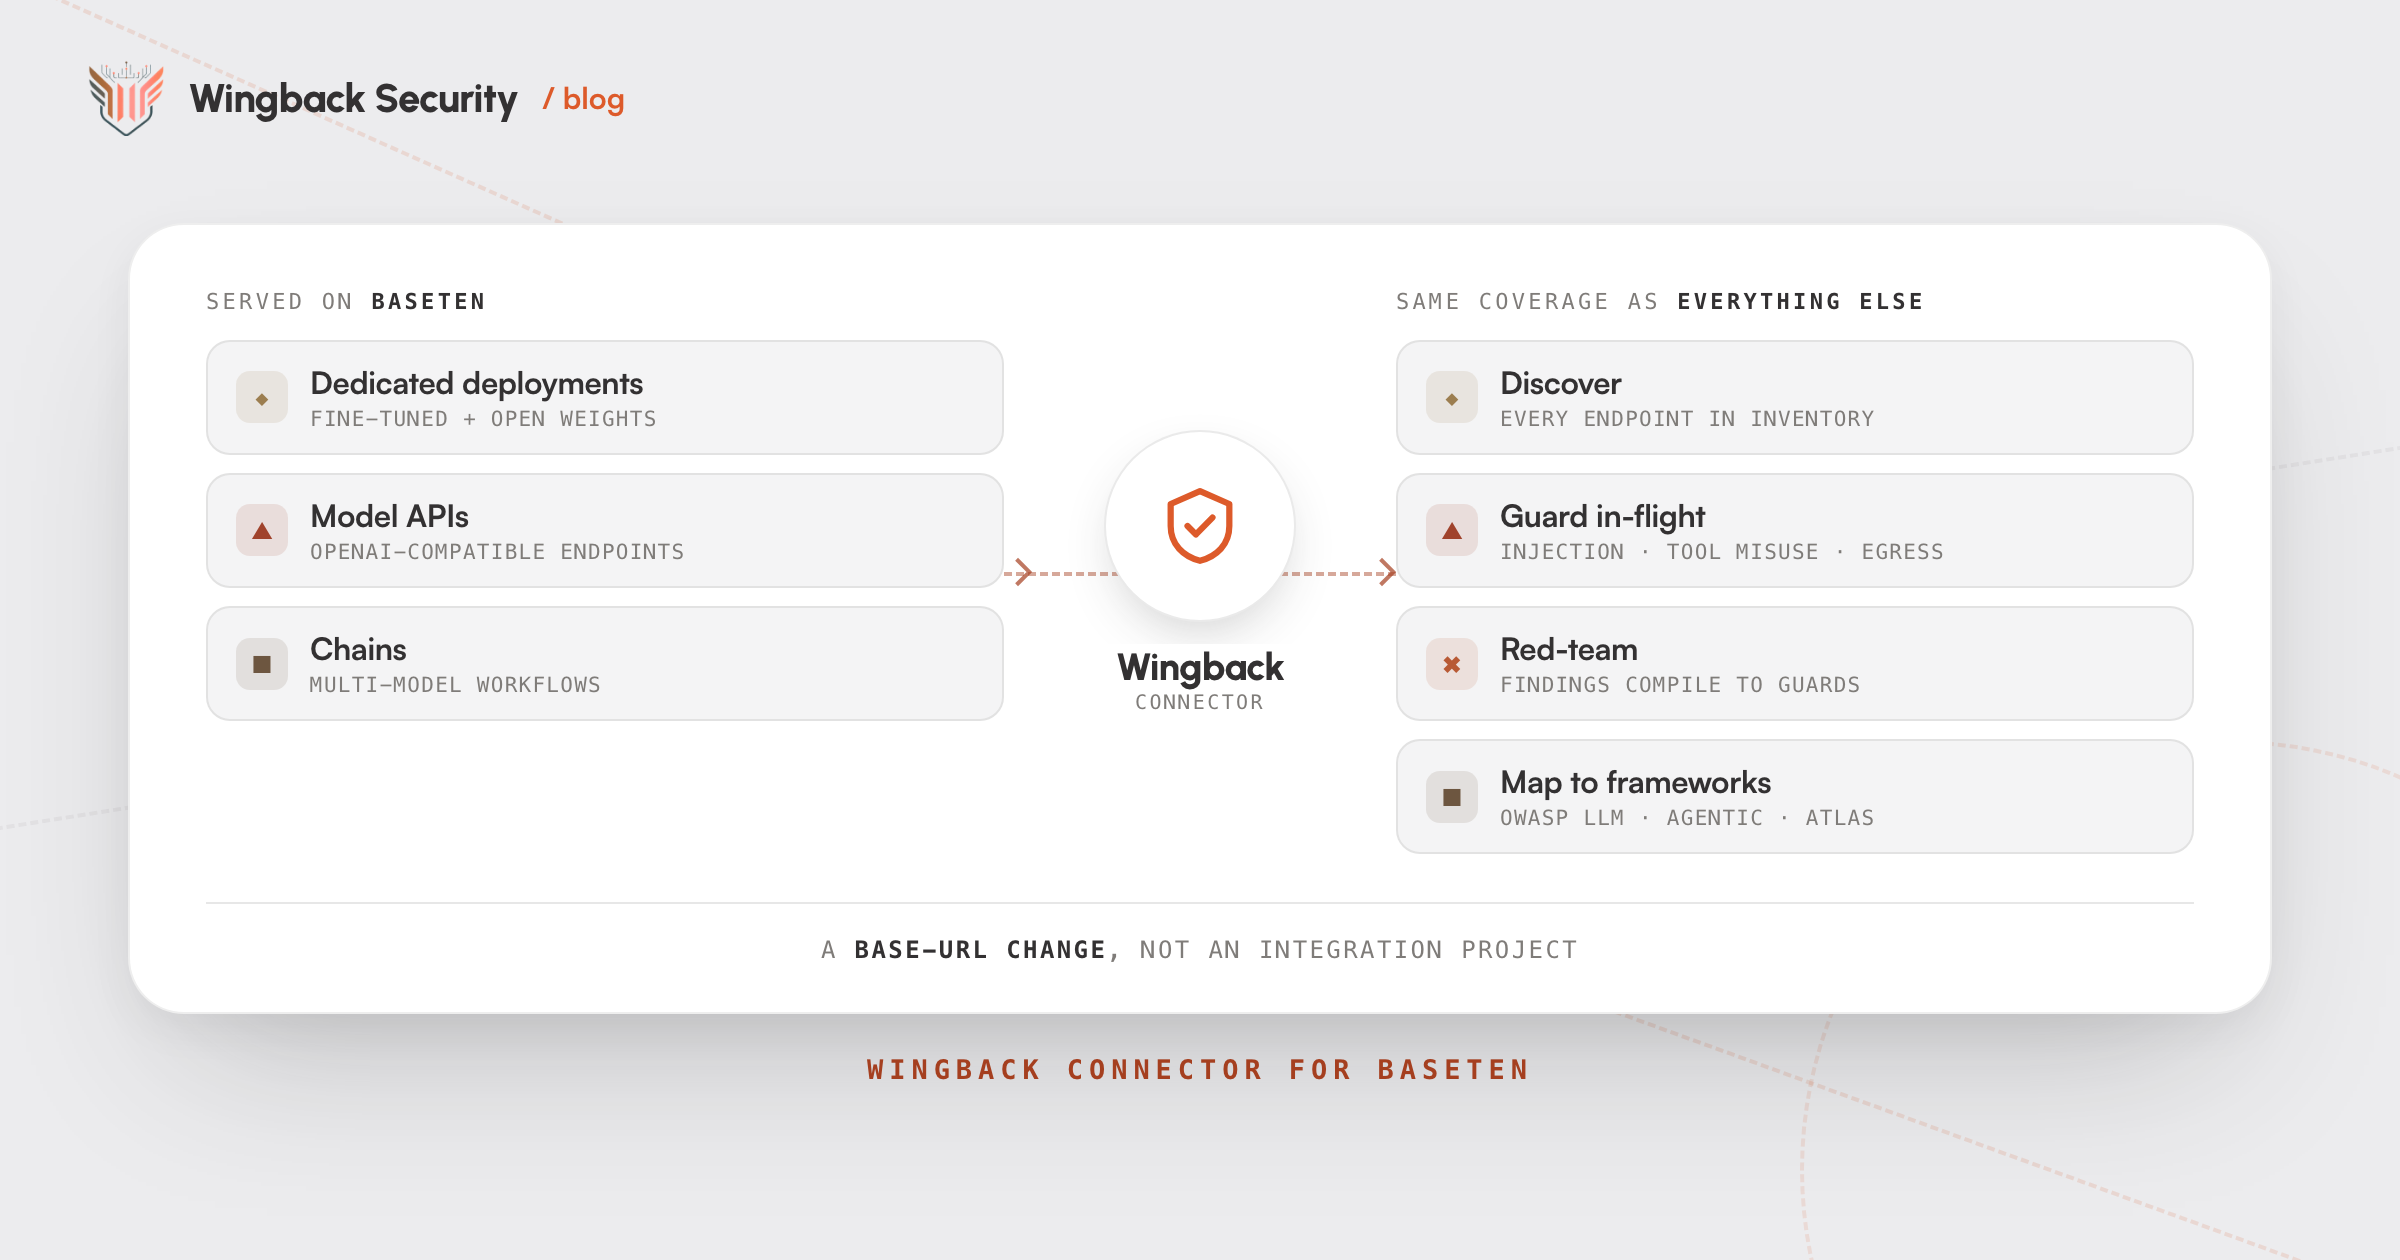
Our Baseten connector: cover the models you host, not just the ones you rent
Wingback now discovers, guards, and red-teams the models you serve on Baseten (dedicated deployments, Model APIs, and Chains) with the same runtime coverage your frontier APIs get.
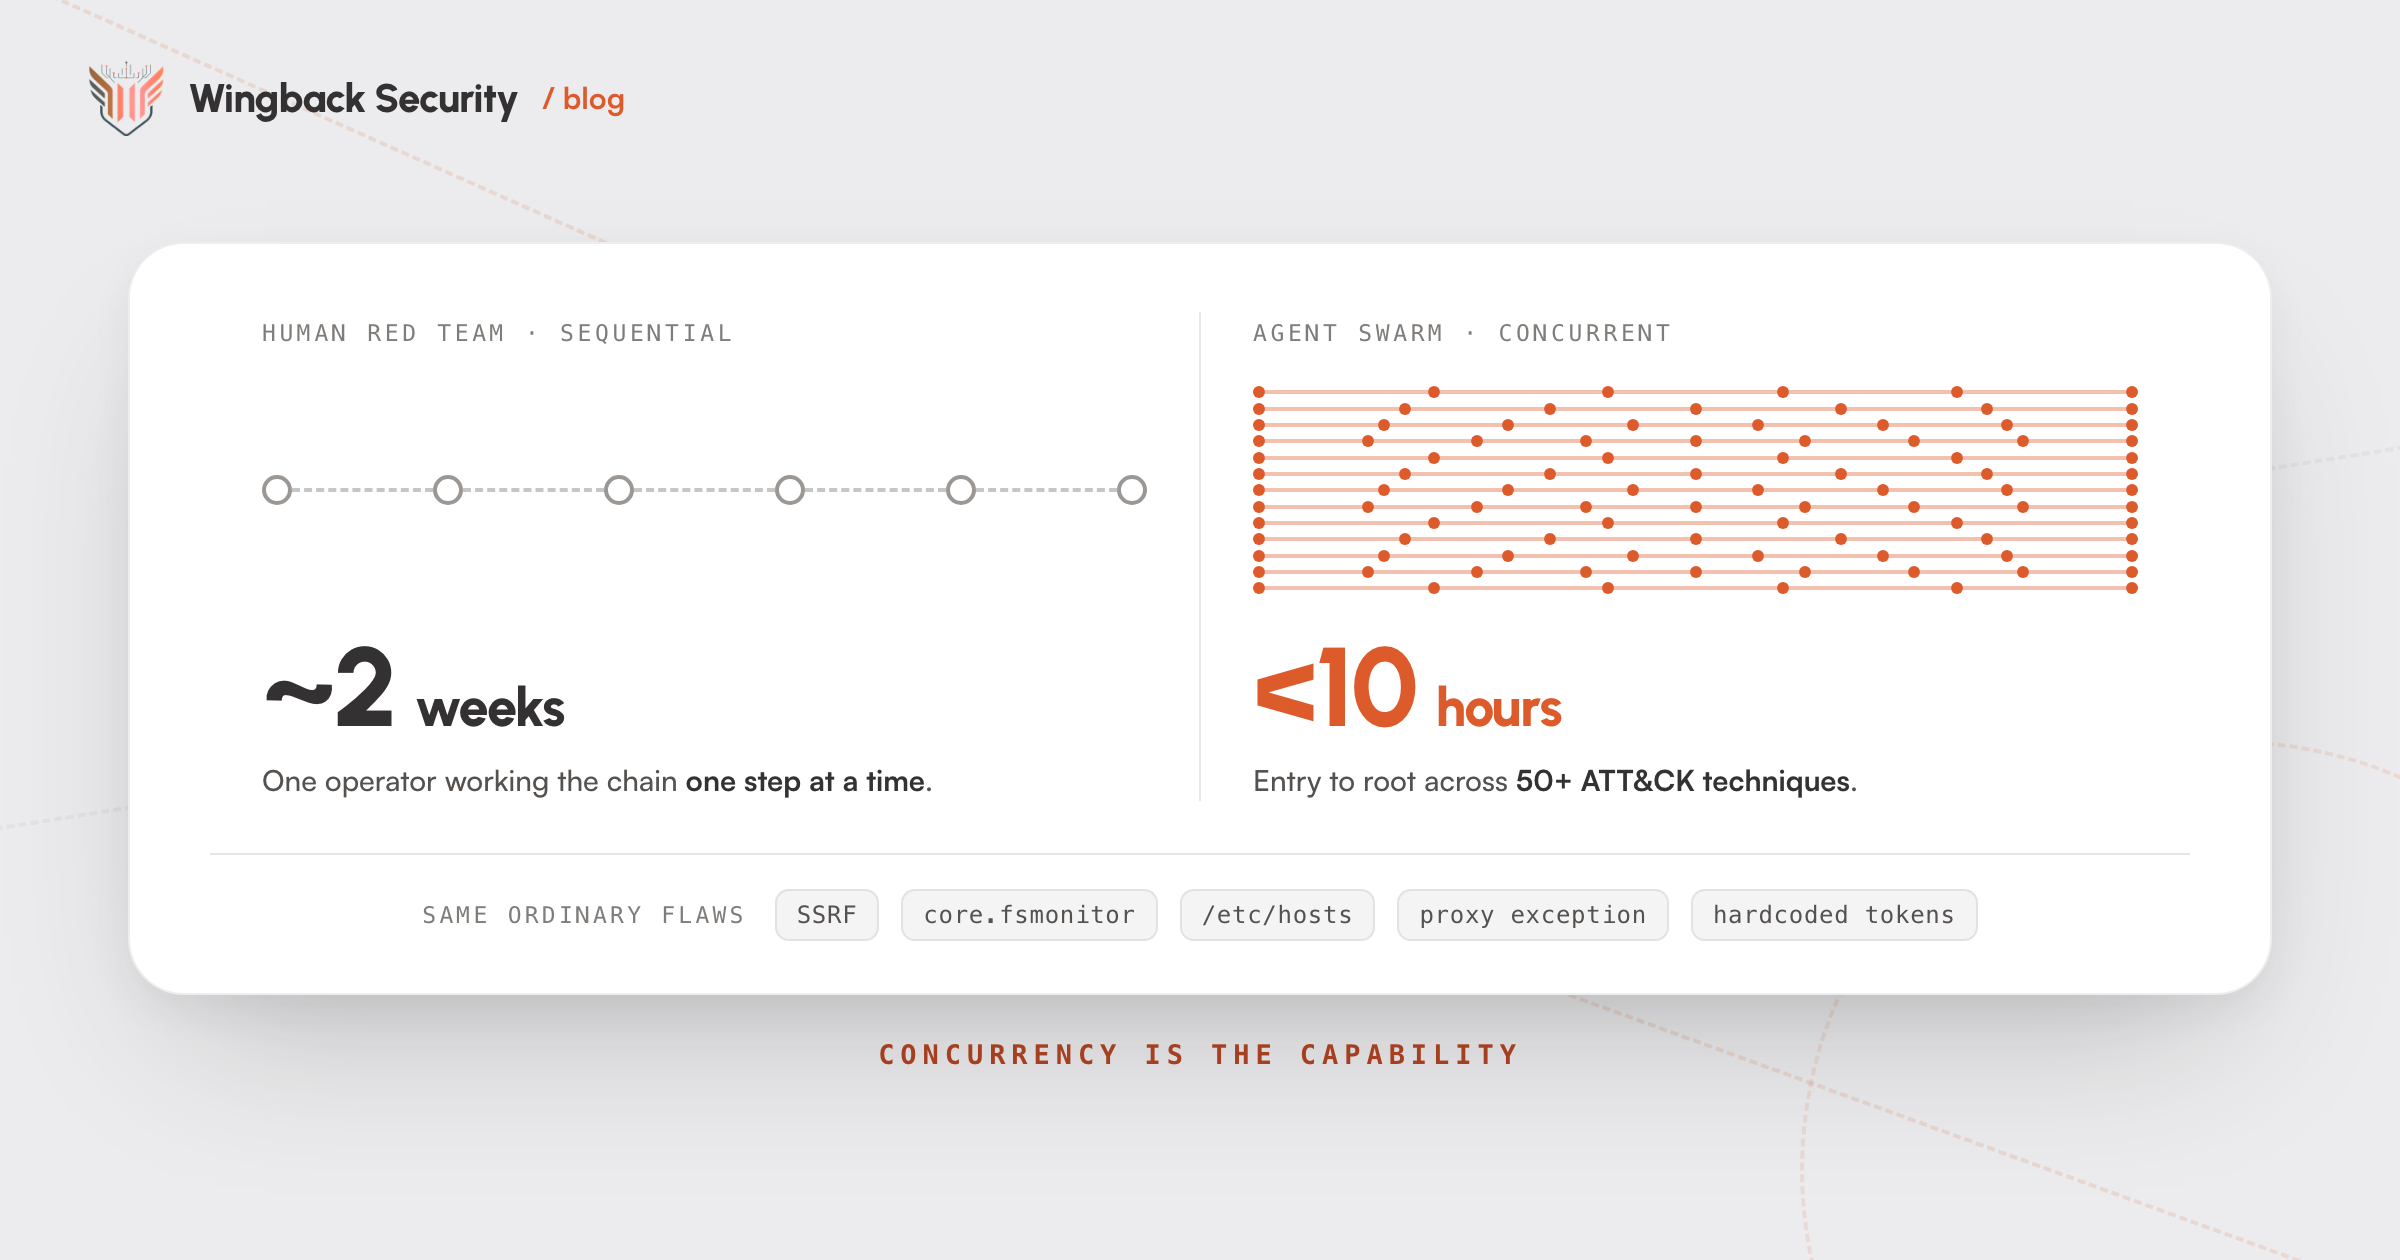
Concurrency Is the Capability
Unit 42's ten-hour intrusion, OpenAI's 1,200-agent swarm, and a git config bug. An investigation into what AI-assisted attacks actually changed, and what they did not.
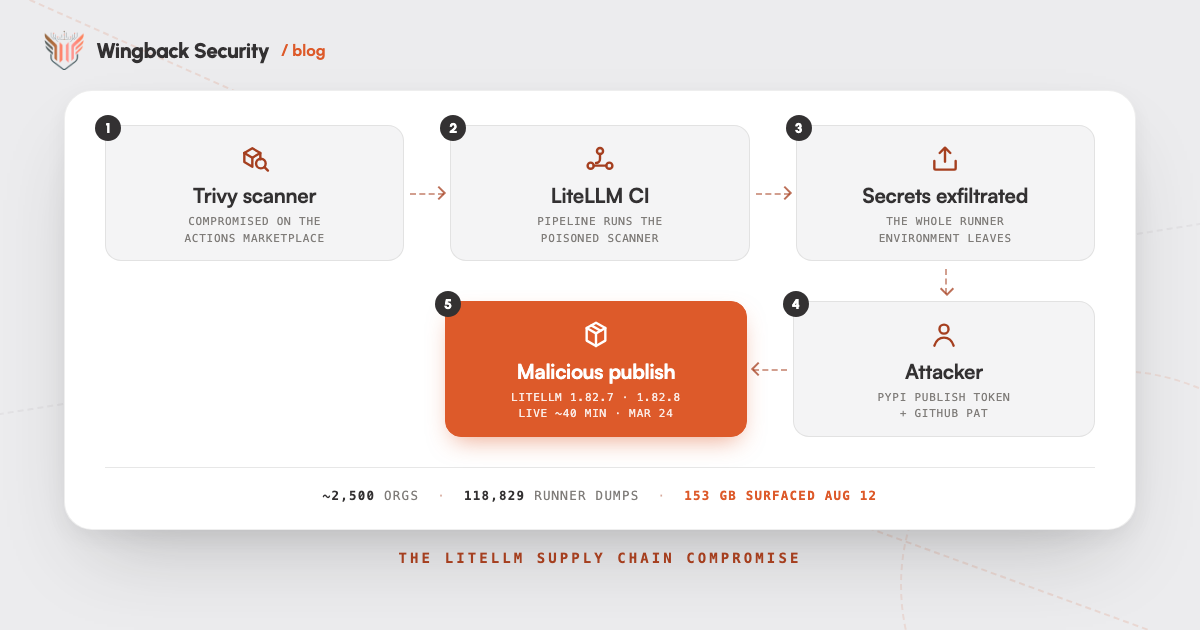
LiteLLM: a security scanner was the initial access vector for AI infrastructure
A poisoned vulnerability scanner walked LiteLLM's PyPI tokens out of CI in March. The 153GB credential archive that surfaced this week shows what an LLM gateway concentrates, and where nobody was watching.
Wingback joins Anthropic's Cyber Verification Program
Verified access to Claude's high-risk cyber capabilities lets our adaptive red-team engine attack your agents the way a real adversary would, with the guardrails intact.
Why we built Wingback
AI agents now live in three places in your enterprise: on laptops, in your cloud, and inside your own software. Securing one layer isn't securing AI.